Certified DevSecOps Course
Build Security into CI/CD, Applications & Infrastructure
- Live Instructor-Led Training (35+ Hours)
- Learn from Industry professionals with 7+ Years of Experience
- Work with Tools such as Jenkins, Docker, Ansible, ZAP, Burp Suite & AWS
- Hands-On Labs Across Threat Modelling, SAST, DAST, IaC, Containers & Vulnerability Management
New Batch is starting on - 08 Nov 2025
Tools Covered
Start Date |
Training Mode |
Batch Type |
Time |
Status |
Enrollment |
|---|---|---|---|---|---|
25 Sep 2026
|
Online
|
Weekend
|
09:00 AM - 12:00 PM
|
- Get Personal training at your available time.
- Get cleared your queries instantly at the call.
- Guaranteed to run the class at your specified time.
- Need the repetition of session? Yes, it'll be available.
- Personal Job assistance, Resume building, Exclusive community access.
Request for Exclusive 1-on-1 training Now!
- Upskill your team with latest AI tools
- Highly Customized solutions for your training requirements
- Skill-specific/ Certification-specific trainings also available
- Secure your organization with latest technologies
Request a Quote today!
- Do you already have customized syllabus which you want to learn?
- Bring the content and we'll teach you!
- Have 1:1 personalized training as per your needs.
- Learn new latest technologies as per your organization.
Request your Customized Training
DevSecOps Training Course in India
Build security into the pipeline—not around it.
A secure application development process involves more than running a vulnerability scan before release. You need to know where security belongs in the SDLC, how to define security gates, automate security checks, investigate findings, and secure the infrastructure that runs your applications. This DevSecOps course takes you through those practices across the CI/CD lifecycle.
You’ll learn threat modelling, SAST, DAST and runtime analysis, integrating them into CI/CD pipelines. The DevSecOps course also covers IaC, Ansible, Packer, Docker security, secrets management, patching, monitoring and vulnerability management, with hands-on labs using tools like ZAP, Burp Suite, Vault, Consul and DefectDojo.
Choose your payment option and start NOW
Choose whatever fits your requirements and budget. For any other seasonal offers, reach out to us!!
DevSecOps Course
Customize Your Training
Make a bundle and share it with usWhat Is DevSecOps?
DevSecOps is an approach to software development where security is built into the development and delivery process rather than being treated as a final checkpoint before release. It brings security considerations into the same workflow used to plan, develop, test, deploy, and maintain applications. The goal is not simply to find vulnerabilities, but to make security part of how software is designed and delivered.
In traditional development, security is often addressed late in the release cycle. DevSecOps brings security earlier into the workflow and uses automation across development, testing, deployment, and maintenance. The DevSecOps course by BlueXploit Cybersecurity Solutions focuses on how this approach works in practice. You’ll learn how security can be incorporated into CI/CD workflows, how different security gates fit into the Secure SDLC, and how findings can be handled within an automated pipeline.
Pre-Requisites for the DevSecOps Training course
- Basic understanding of application security practices is expected.
- Familiarity with concepts such as SAST and DAST is recommended.
- The course then builds on these fundamentals to cover security across the development and delivery lifecycle.
DevSecOps Course Objectives
- Understand DevOps and DevSecOps principles and how they differ.
- Learn how security fits into the Secure SDLC and CI/CD pipeline.
- Work with threat modelling, SAST, DAST and Runtime Analysis.
- Learn security practices for Infrastructure as Code, containers and secrets.
- Understand patch management, security monitoring and vulnerability management.
What tools are covered in the DevSecOps course?
- GitHub, GitLab and Bitbucket for version control.
- Jenkins, Travis CI and GitLab CI for CI/CD.
- Docker for containerisation and container security.
- Ansible and Packer for infrastructure automation and hardening.
- OWASP ZAP and Burp Suite for dynamic application security testing.
- Bandit, ThreatSpec, Vault, Consul, Clair and DefectDojo through different modules and labs.
Who should take this DevSecOps course?
- Security professionals who want to understand how security is integrated into development workflows.
- Developers interested in incorporating security into CI/CD.
- DevOps professionals looking to add security controls to their pipelines and infrastructure.
- Application security professionals who want to automate security testing and vulnerability management.
- Learners who already have a basic understanding of application security practices such as SAST and DAST.
Job Roles After Completing This Course
- DevSecOps Engineer
- Application Security Engineer
- Cloud Security Engineer
- Security Automation Engineer
- DevOps Security Engineer
- Vulnerability Management Analyst
- Infrastructure Security Engineer
Still not Sure?? Schedule a FREE Demo Session
BlueXploit Post-Training Support
How BlueXploit is best for your Cybersecurity Career?
Resume format for Guaranteed Shortlisting
LinkedIn & Naukri Profile Optimization
Interview Preparation
Lifetime Mentoring
Direct Job opportunities
Premium Community Access
See What Our Students Has To Say....
Companies where our students are placed
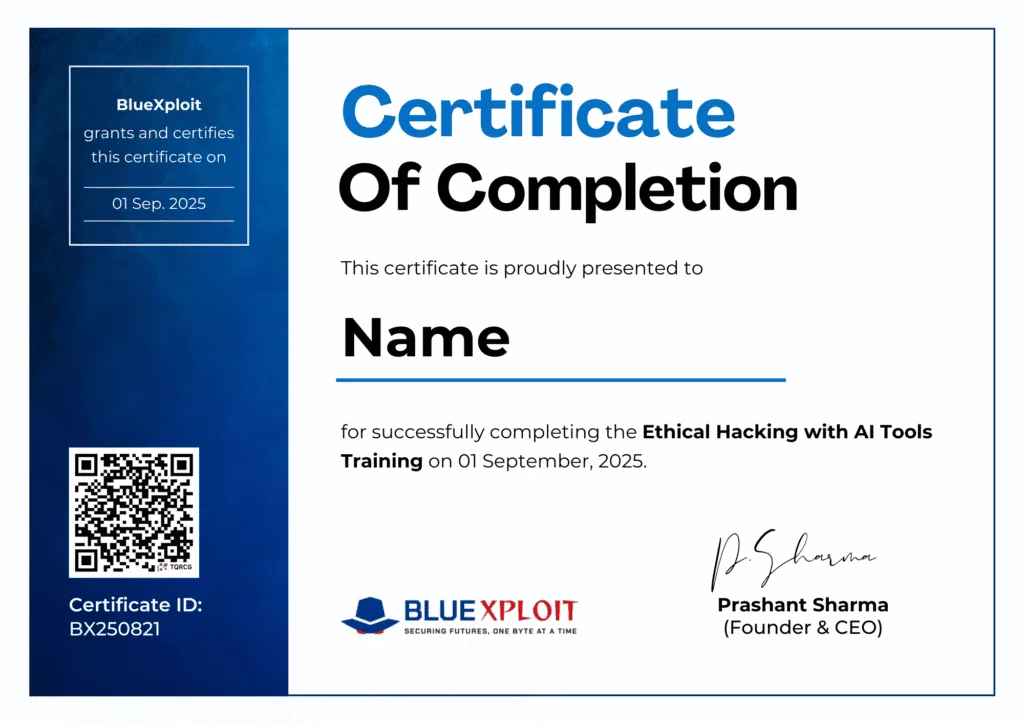
Join the course and avail "BlueXploit Certified DevSecOps Expert (CDE)" Certificate
FAQ
Frequently Asked Questions
Yes, provided you have the required application security fundamentals. The course begins with DevOps and DevSecOps concepts before moving into Secure SDLC, CI/CD security, threat modelling and security testing.
The training includes hands-on labs throughout the syllabus. You’ll create a CI/CD pipeline, automate security requirements and findings, configure security scans, harden infrastructure, audit Docker environments and work with vulnerability management.
The course includes hands-on labs covering CI/CD pipelines, Threat Modelling as Code, SAST, DAST, infrastructure hardening, Docker security, secrets management and vulnerability management.
Yes. You’ll learn approaches to organisational vulnerability management, including handling false positives and false negatives and defining metrics for different teams. The syllabus also covers security monitoring with Elasticsearch, Logstash and Kibana and includes a DefectDojo lab.
Yes. You’ll learn how static and dynamic analysis can be incorporated into CI/CD pipelines. The hands-on work includes writing custom Bandit checks and configuring OWASP ZAP and Burp Suite scans.
Yes. You’ll learn approaches to organizational vulnerability management, including handling false positives and false negatives and defining metrics for different teams.
This DevSecOps Course also covers security monitoring with Elasticsearch, Logstash and Kibana and includes a DefectDojo lab.
Many DevSecOps courses focus primarily on concepts or individual security tools. This course takes a broader approach, covering how security fits across the Secure SDLC and CI/CD pipeline—from security requirements and threat modelling to testing, hardening, monitoring and vulnerability management.
Yes. The course assumes a basic understanding of application security practices such as SAST and DAST, so you are not starting from the very beginning. It builds on those fundamentals and moves into their integration with CI/CD, custom security checks, threat modelling and automated security workflows.
The labs focus on applying DevSecOps practices rather than simply demonstrating tools. You’ll work on CI/CD pipeline creation, Threat Modelling as Code, custom SAST checks, DAST configuration, infrastructure hardening, Docker security, secrets management and vulnerability management.
The course shows you how security activities can be incorporated into a development and delivery workflow instead of being handled separately. You’ll work with security gates, automated testing, security findings, infrastructure hardening and vulnerability management within the DevSecOps process.
You can call our team on +91 8791620202 or mail on support@bluexploitcybersecurity.com or can fill the Enrollment form.
BlueXploit Cybersecurity Community
Join the Evergrowing Global Community of Industry Professionals
Connect with skilled cybersecurity professionals, where you’ll connect, learn, and grow together. Gain insights from bi-weekly knowledge-sharing sessions, daily cybersecurity resources, and exclusive monthly bootcamps. Plus, never miss an opportunity with weekly job alerts designed to keep your career on track.